Ugrás a fő tartalomra

Techtorial 2023

 Hello Folks!

I am going to write a short post about my Hungarian Techtorial 2023 experiences. Why am I do it? Because I have not have new topic in CCIE learning path. Last time I posted about BGP and IGP and I could write a deep-dive thing about them, but I think that can not be interesting in this platform. So I decided it that I write a a little about my Techtorial experiences. 


Ok! What is techtorial?

I think the Hungarian Cisco Techtorial was a network engineering celebrity day, like the ITBN for Security Engineers. My first event was at 2015 when I worked for the MT (Hungarian Telecom). It was a great time to talk with very smart people about the newest technologies, I learned many new technologies. Nowdays the event is good, but I can not see the twinkling and sparkling behind the programs, but I changed not the event. (If it will be 2 days program again with hotel room... ;) )

What is SD-WAN? | NetworkAcademy.io

In this year, the event was kept in the Etele Plaza Cinema (yeah like in 2022). There was many interesting topic in the program, my personal favorite was the  B. Áron's (cisco) SD-WAN presentation. It was a great summary about, where the cisco is in this technology, which are the development vectors in this topic. The second interesting presentation was also from Áron's SDA-fabric design considerations presentation. I was a good summary about the new network architecture of SDA (LISP Pub/Sub) or the new feature of DNA Centers.
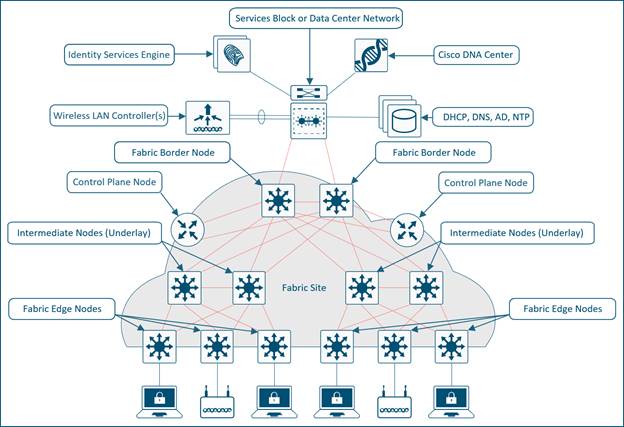
Cisco SD-Access Solution Design Guide (CVD) - Cisco

I really would like to join the Segment Routing topic, but I have not enough time... so I have to be satisfied with the presentation pdfs.

Instead of the SR topics accidentally I joined to an interesting WiFi backhaul presentation which was fascinating. In a short: WiFi APs can join on wireless mode to each other, and they can automatically build an MPLS network. What a great presentation of the Service Provider technologies can integrate in the enterprise or industry networks.

https://www.cisco.com/c/en/us/products/wireless/ultra-reliable-wireless-backhaul/index.html

Ok the real reason why I am write this post is:

I kept my own presentation about the Automation in the Enterprise Network on based DevNet service.

Here is a little  summary about it:

It has been already done by the Robot!

So what the Robot have to do?

Anything or everything!

Good question! I tried to present to the public, the enterprise system integration can be or can not be different from the innovation process. What is the differences? It can be the same!


Are there any universal process for enterprise innovation?


 How can be a prototype developed?


 Can we develop our own Robots?


And so many marketing element, what I do not want to present in here...

Read it on the 99999 webpage! (if it available)

So my topic was the automation possibilities of the IT (Network) infrastructure, and I show a demo about or WEBEX based ISE integration.


 Yeah here I am, that gray haired fat guy... that's all Folks!

See yo in the next post! (I hope it will be an CCIE topic)


Érdekesebb bejegyzések

FortiGate - SEC előfizetésen túl

Végre megvan az új NGFW a cégben, megvettétek 3 vagy 5 éves enterprise vagy utp bundle-ben és biztonságban érzitek magatok (Szárazabb, magabiztosabb érzés nem?), hiszen van IPS , webfilter, antivirus stb... security profile, ami megvédhet az ismert támadásokkal szemben. Nyugodtan "hátradőltök" és készítitek az auditokhoz szükséges riportokat a FortiAnalyzerből... biztonságban eltelik az 5 év és "váratlanul ér" előfizetés megújítása, nincs budget, pánikolva néztek valamilyen alternatív alsópolcos megoldást, amit még be tudtok szerezni és kidobnátok a jó hardvert, ami éveken keresztül stabilan szolgált titeket... Ne tegyétek! Mutatom milyen feature-ket használhattok tovább ingyen: Persze az alábbi megoldások nem minden végfelhasználónak jelentenek megoldást a problémákra és kihívásokra, de KKV szektorbnan vagy olyan esetekben, ahol nem szükséges IPS, anitvirus, webfilter, még jól használhatók tovább ezek a hardverek/szoftverek előfizetések nélkül. Fontos, ha egyébként...

CCIE #69065 - SRv6, most már tényleg átállunk IPv6-ra?

Röviden: NEM Hosszabban: Nem egészen, a teljes IPv6 átálláshoz nem elegendő csak a hálózat eszközök (több mint 10 éve meglévő) képességeit kihasználni, hanem ehhez a teljes informatikai iparágnak kellene paradigmaváltáson átmenni, ami azt jelenti, hogy a felhasználói (business és consumer) alkalmazásoknak minden kétséget kizáróan nagy rendelkezésre állással kellene támogatni a TCP/IPv6 stack-et (sok helyen tapasztaltam, hogy még a TCPv4-et sem sikerült minden kétséget kizáróan jól implementálni, de még operációs rendszerek szintjén sem). Viszont a szolgáltatók a publikus IPv4 kifogyást megelőzendő a szolgáltatói környezetet már migrálhatják IPv6-os hálózatra, ami megfordíthatja a korábbi, IPv6 over IPv4 (MPLS vPE6) vagy dual-stack (Internet) architektúrát  akár natív  IPv4 over IPv6 (SRv6) jellegű felállásra. A teljes képhez sok mindent tisztába kellene tenni, de élek az alkotói szabadsággal és úgy vagyok vele, hogy nem célom most itt mindenkit telekommunikációs mérnökké avanz...

Fortinet minősítési rendszer változások - avagy a FortiThanos lecsap

 A Fortinet bizonyos időszakonként megváltoztatja a vizsga rendszerét és minősítési rendszerét...  Amikor 2018-ban elkezdtem foglalkozni a Fortinet Network Security megoldásaival, akkor még "lázasan" NSE4 vizsgára készültem, ami FortiGate alapok mellett néhány advanced témát is érintett.  Ekkor már átesett a Fortinet egy vizsgarendszer átalakításon, és korábban FCNSP (Fortinet Certified Network Security Professional) minősítések lettek NSE4 minősítéssé. Még ebben az időszakban terveztem tovább lépni NSE7 szintre, ami akkor egy vizsgával megléphető volt aztán bummm! Jött a vizsgarendszer átalakítása és a korábban NSE1 - 8 minősítések új rendszerbe kerültek.. Az NSE1 - 3 -ből lett a az FCF ás FCA azaz Foundamental és Associate minősítések (ezek online elvégezhető tanfolyamok és nem proctored vizsgák) NSE4 + NSE5 vagy NSE6-ből lettek az az FCP minősítések (Professional) NSE7 vizsgákból illetve azok kombinációiból lettek az FCSS minősítések (Specialist)  NSE8 pedig FCX a...

CCIE SP v5.x Lerning journey #xxxxx3 Deep Dive of IGPs: OSPF part 1

 Everything what you do not want know about the OSPF! In a Service Provider network, one of the most important part is the IGP (Interior Gateway Protocol). Why? Because the network core convergence and routing strategy is depend on the IGP routing rules. If the IGP can not support some features what  are needed for the traffic engineering, it could be a  future operation or development problem. So SPs select IGPs which are satisfy every operational and business needs, and it will be a future proof protocol. Many of service providers typically choose OSPF or ISIS for IGP, because: - they are RFC and ITU-T conform, vendor independent protocols (in general) - they support MPLS traffic engineering features (OSPF opaque LSA 10 11) - link-state routing protocols, which means  that these can provide faster convergence than vector-path or distance vector protocols, and they are more scalable. What is OSPF?  OSPF (Open Shortest Path First) protocol is a dynamic link-stat...